The Future of B2B Data: AI, Automation, and Compliance
How AI and automation are changing B2B data collection, and why compliance keeps that data trustworthy.
Read article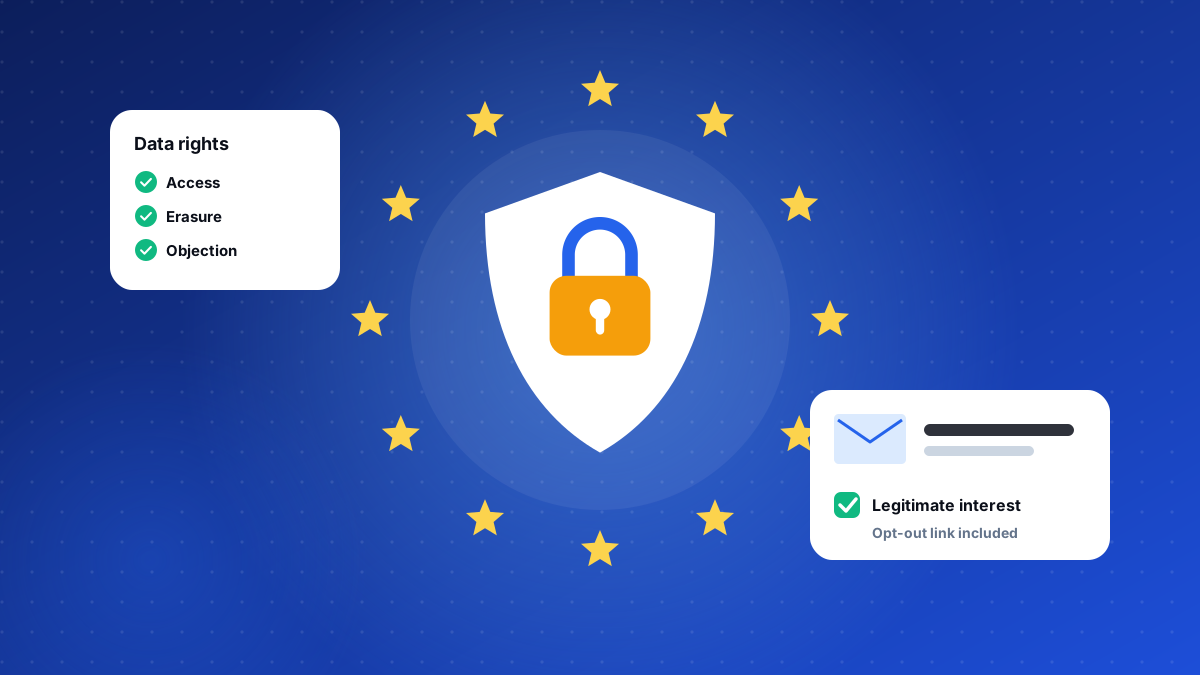
GDPR gets treated as a marketing problem, but it applies just as much to sales outreach. This is not legal advice, just a practical look at how sales teams commonly stay on the right side of the rules while still prospecting effectively.
GDPR does not ban cold outreach to businesses outright, but it does require a lawful basis for processing someone's personal data, which includes their name, email, and job title. For most B2B cold outreach, that lawful basis is usually legitimate interest, not consent, provided a few conditions are met.
A list with no documented source or consent trail is a compliance and a deliverability risk.
Every outreach email needs a simple, working way to say stop.
Continuing to reach the same person through another channel after they have opted out undermines the whole basis for legitimate interest.
Special category data, like health information, needs a different and stricter basis than ordinary business contact data.
Related service
Customer data decays over time. We validate, standardize, deduplicate, and enrich your CRM so your team engages the right people with the right details.
Keep reading
How AI and automation are changing B2B data collection, and why compliance keeps that data trustworthy.
Read articleWhy a curated B2B database and a raw contact list lead to very different outreach results.
Read articleWhat DUNS registration means for transparency, verification, and enterprise-grade data services.
Read articleAsk us anything
From list building to CRM cleanup, our researchers are happy to talk through what will work for you.
We use cookies to provide essential website functionality, improve your experience, understand website performance, and support our marketing activities.
You can choose which types of cookies you allow. Essential cookies cannot be disabled because they are required for the website to function properly.
These cookies are necessary for core website functions, security, navigation, and your cookie preferences.
These cookies help us understand how visitors use our website, such as which pages are visited and how users interact with our content. This helps us improve our website and services.
These cookies may be used to understand advertising and campaign performance and provide more relevant communications or content.
Locked off because your browser sent a privacy opt-out signal or you opted out of sale or sharing.
These cookies allow the website to remember certain preferences and provide enhanced functionality.
You can change your cookie preferences at any time through the Cookie Settings option on our website. For more information, please see our Cookie Policy and Privacy Policy.